Unauthorized changes to system files are now caught as they happen, with the user and process behind each one. Atatus File Integrity Monitoring (FIM) records every file creation, modification, move, permission change and deletion in the paths you choose on your Linux hosts.
Each event comes with a severity, a risk score and a suspicious-activity flag, along with the file's permissions, owner and size after the change. FIM is part of Atatus Cloud SIEM, so file events feed the same detection rules and alerts as the rest of your security data.
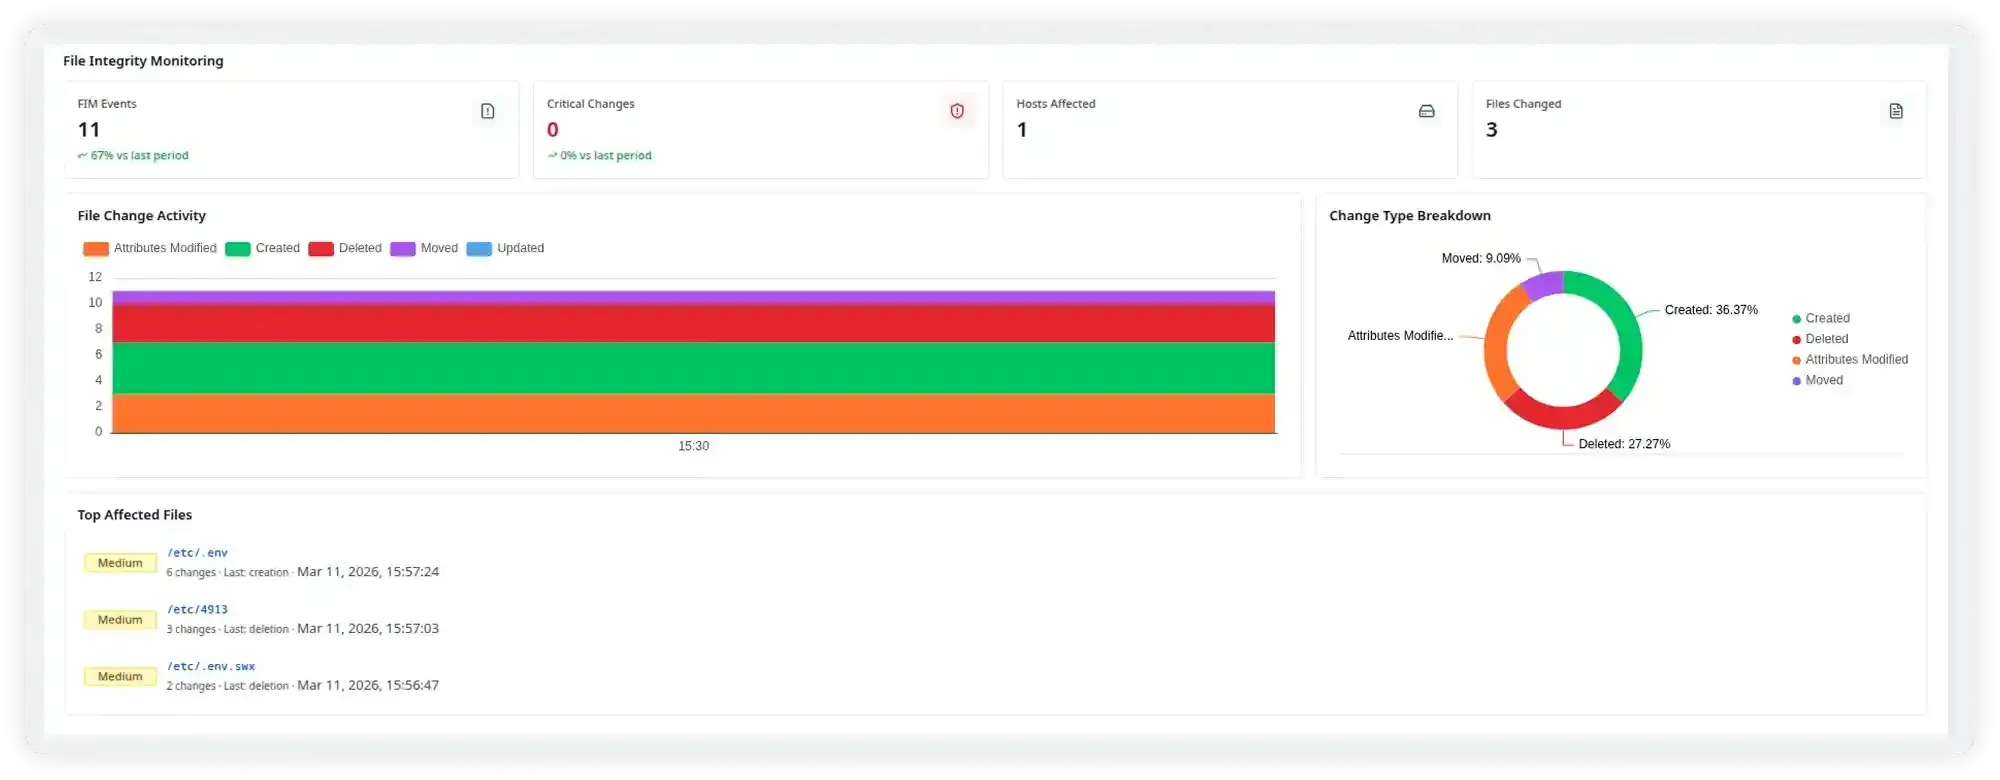
What File Integrity Monitoring gives you
- Real-time change detection: Watch the files and directories you list, such as /etc and /usr/bin, and record each change with its time, user, process and host. FIM runs in the Atatus Infrastructure Agent 4.2.0 or later.
- Context for every change: Each event shows the change type, host, user, process and command line, the file's permissions, owner and size, and a risk score out of 100 for faster triage.
- Detection rules and alerts: Built-in rules flag changes to sensitive files such as /etc/passwd, /etc/sudoers and sshd_config. Use file events in your own Cloud SIEM detection rules, and send matches to Slack, Microsoft Teams, email or PagerDuty.
- Filter and search: Filter events by severity, event action, file path, host, user or process, and widen the time range when you need to investigate an older change.
- Tune the agent: Choose the hash algorithm, the event backend (fsnotify, kprobes or eBPF), include and exclude patterns, and a scan rate limit to keep overhead low.
- FIM overview: The Cloud SIEM Overview shows FIM events, critical changes, hosts affected and files changed, a file change activity chart by change type and the most frequently changed files.